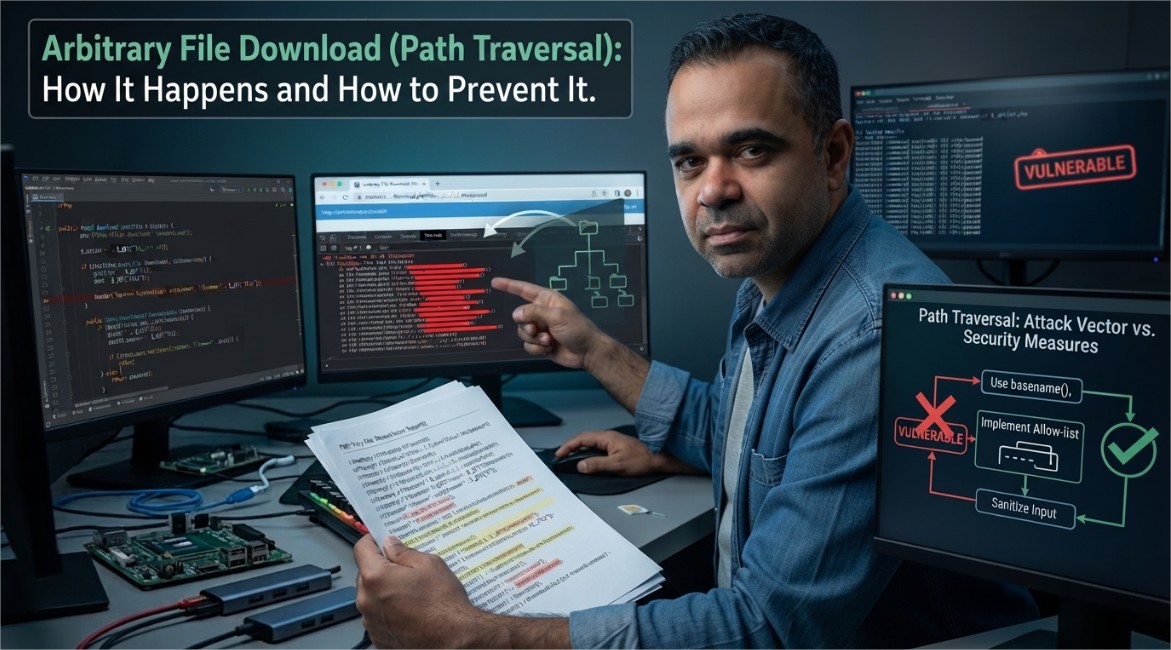
Arbitrary file download — more precisely known as path traversal or directory traversal — happens when a web application lets a user specify a filename to retrieve, but doesn't properly restrict that input to the files it's actually meant to serve. The result: an attacker can potentially retrieve any file the web server process has permission to read, not just the ones the application intended to expose.
Read more: Arbitrary File Download (Path Traversal): How It Happens and How to Prevent It